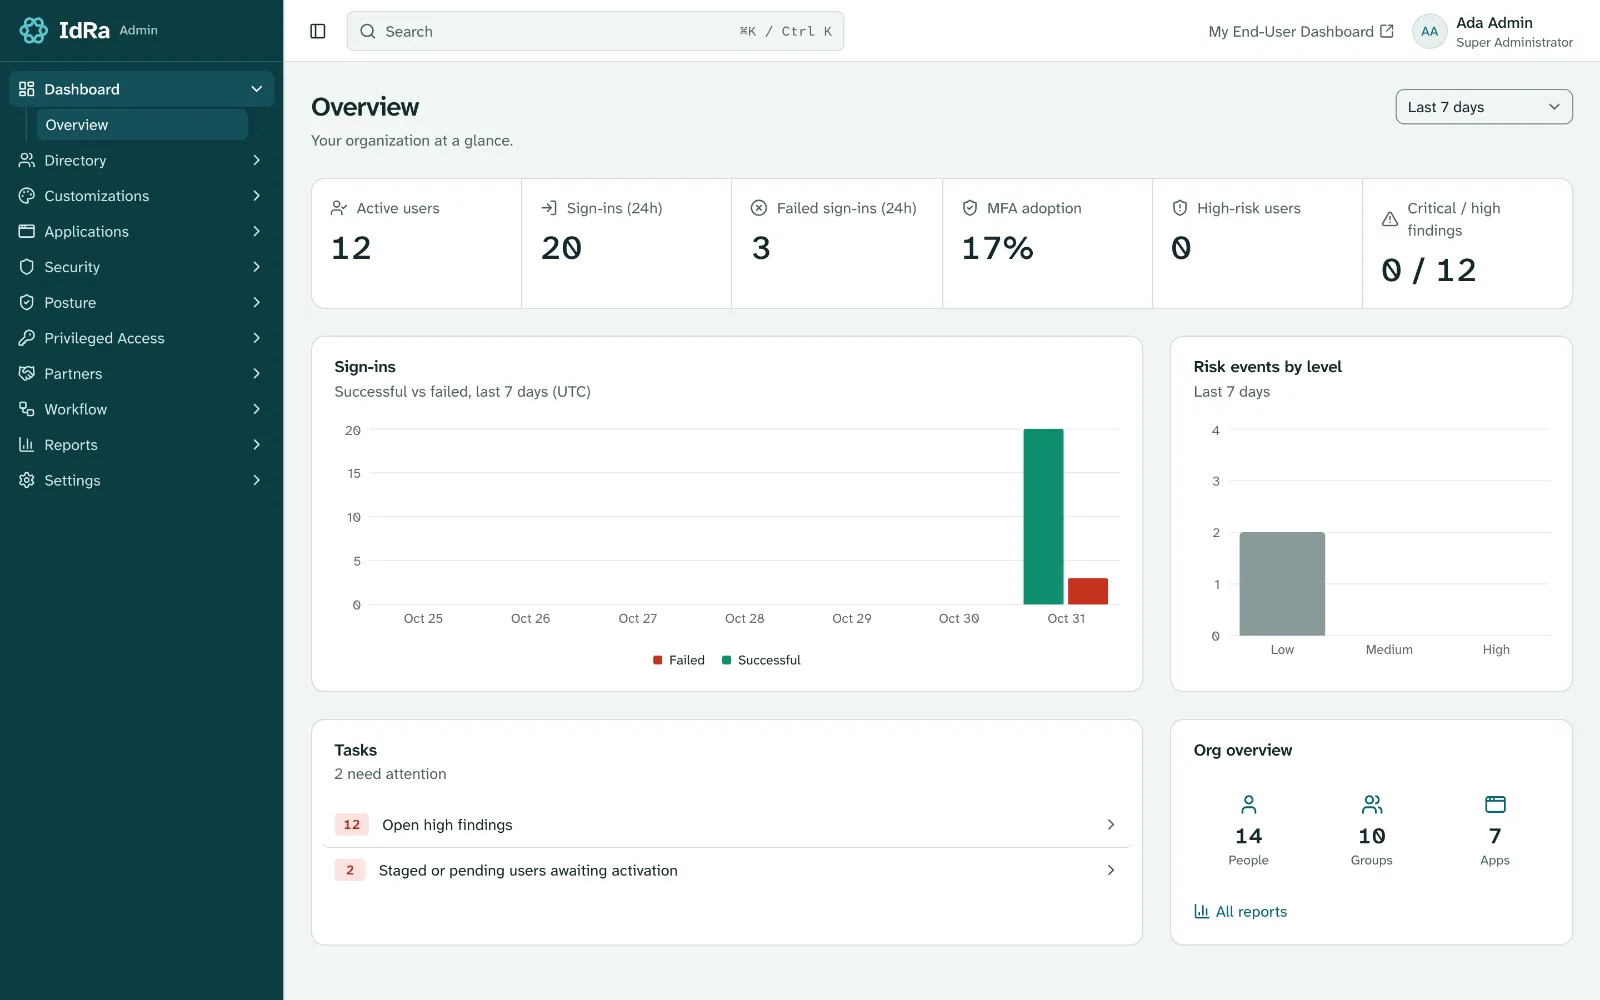
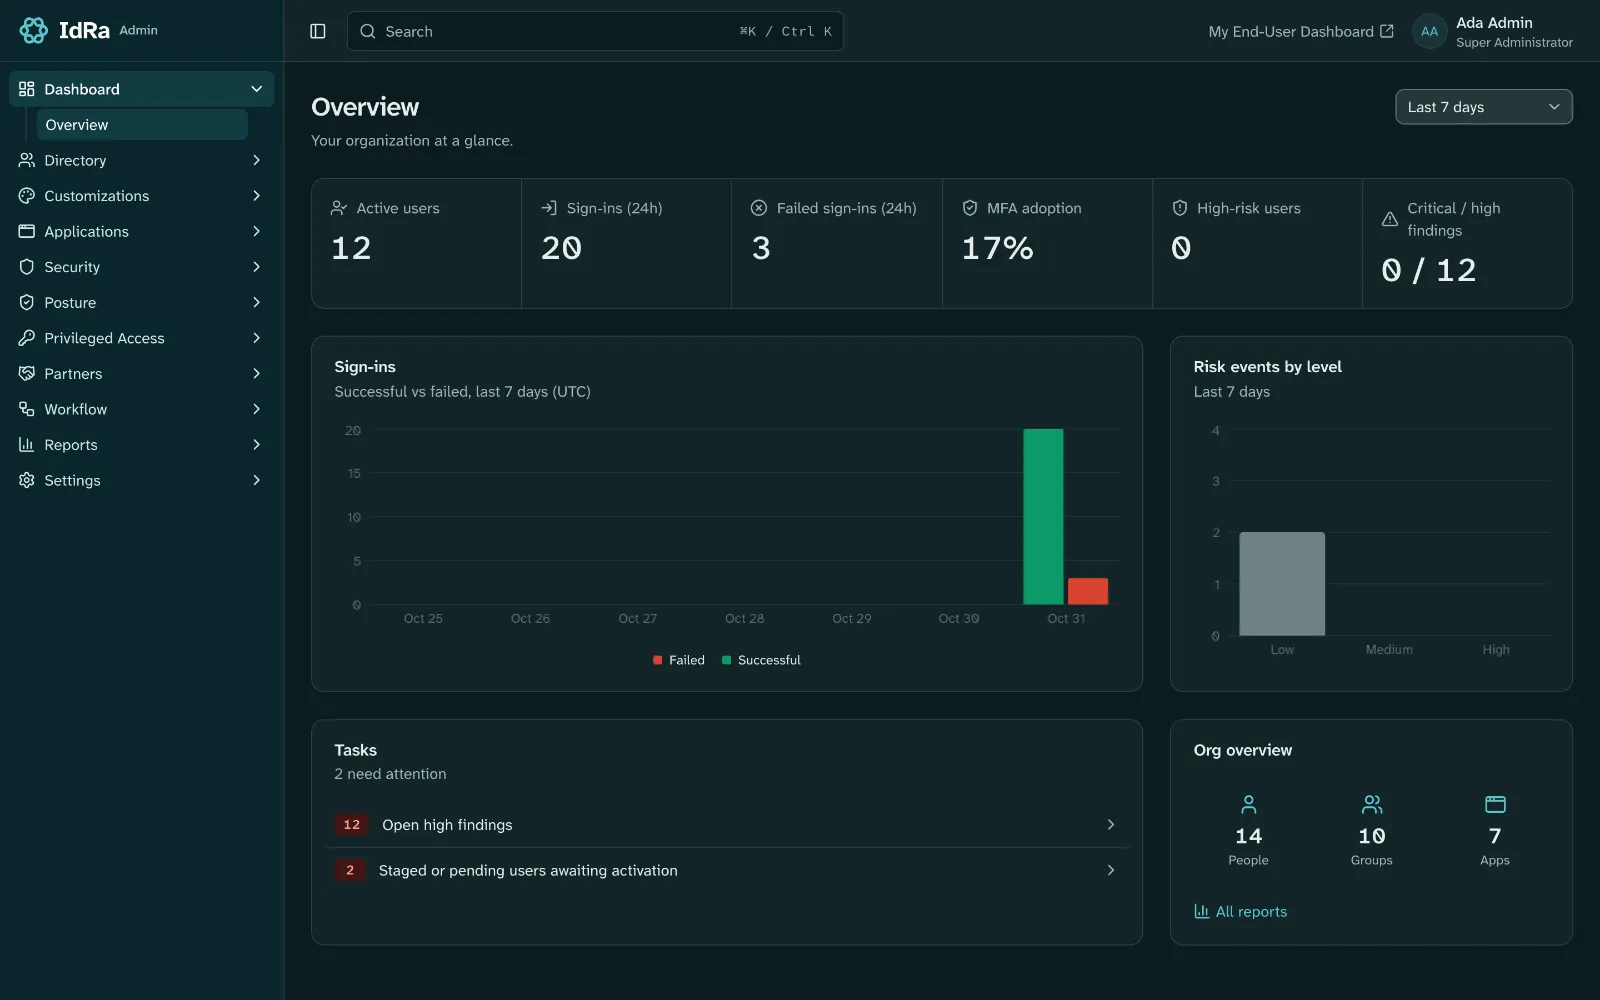
The whole identity stack, in one product.
One directory, one policy engine and one audit log sit under everything here.
Single sign-on
One sign-in for every app, over OIDC and SAML
MFA and adaptive access
Passkeys, push and policies that react to risk
Lifecycle and SCIM
Access that follows people from first day to last
Directory
People, groups, rules and custom attributes
API access management
Authorization servers, scopes and token policy
Device trust
Device checks from your MDM, in sign-in policy
Multi-tenant and partners
A database per organization, a portal per partner
Security suite
Threat protection, posture and privileged access
What every part shares
- An audit log with search, filters, CSV export and an Okta-shaped API
- OIDC, SAML and gateway access all pass through one enforcement point, so assignment, zones and app policy apply the same way
- An admin console that writes changes to the audit log, with MFA required for admins to sign in
- Secrets IdRa manages encrypted with AES-256-GCM
Create your organization.
Pick an address and confirm your email, then sign in as its first admin. A setup wizard takes you through the rest.