Platform / Directory
One record for each person.
People, groups, custom attributes and rules, for every app and policy.
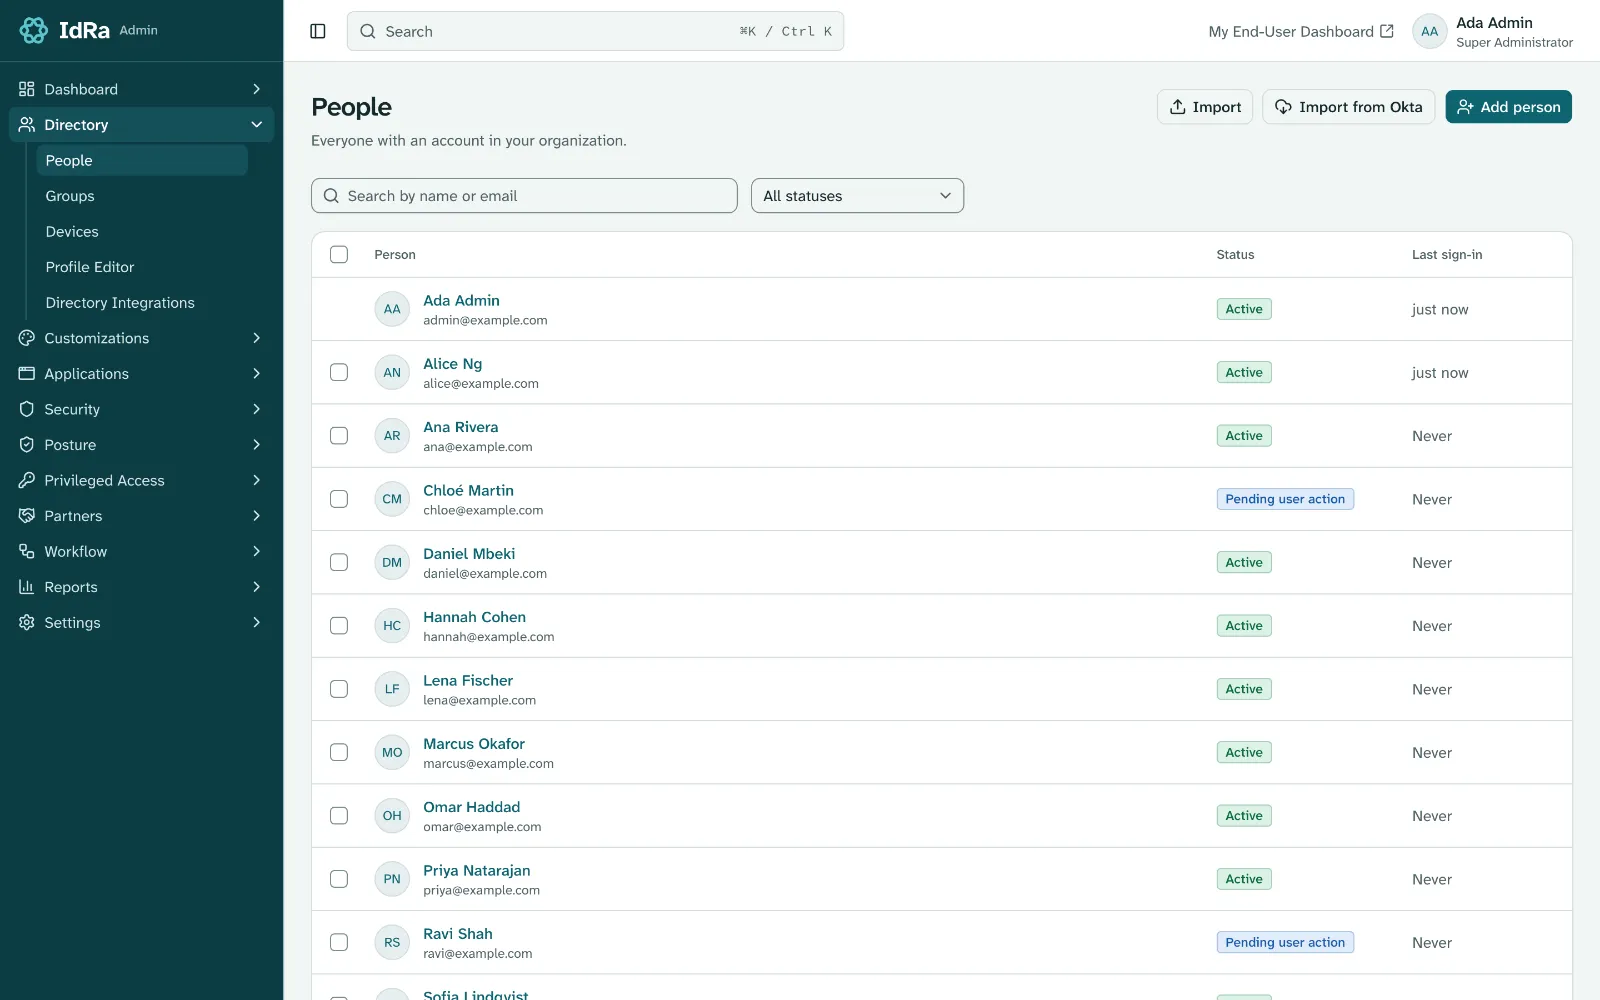
People with a full lifecycle
Staged, active, suspended, deprovisioned: every change is an event in the audit log.
- Custom attributes: text, number, boolean, date and enum
- User types with their own attributes, and linked objects such as manager
- Self-service recovery, which also clears a lockout
- Admin impersonation with a reason, fresh MFA and a log entry
Groups that maintain themselves
Write a rule once and membership follows the data. Every person is also in an implicit Everyone group.
- Group rules that match on attributes, with Okta-style expressions
- Time-limited membership
- Group-based assignment for apps and policies
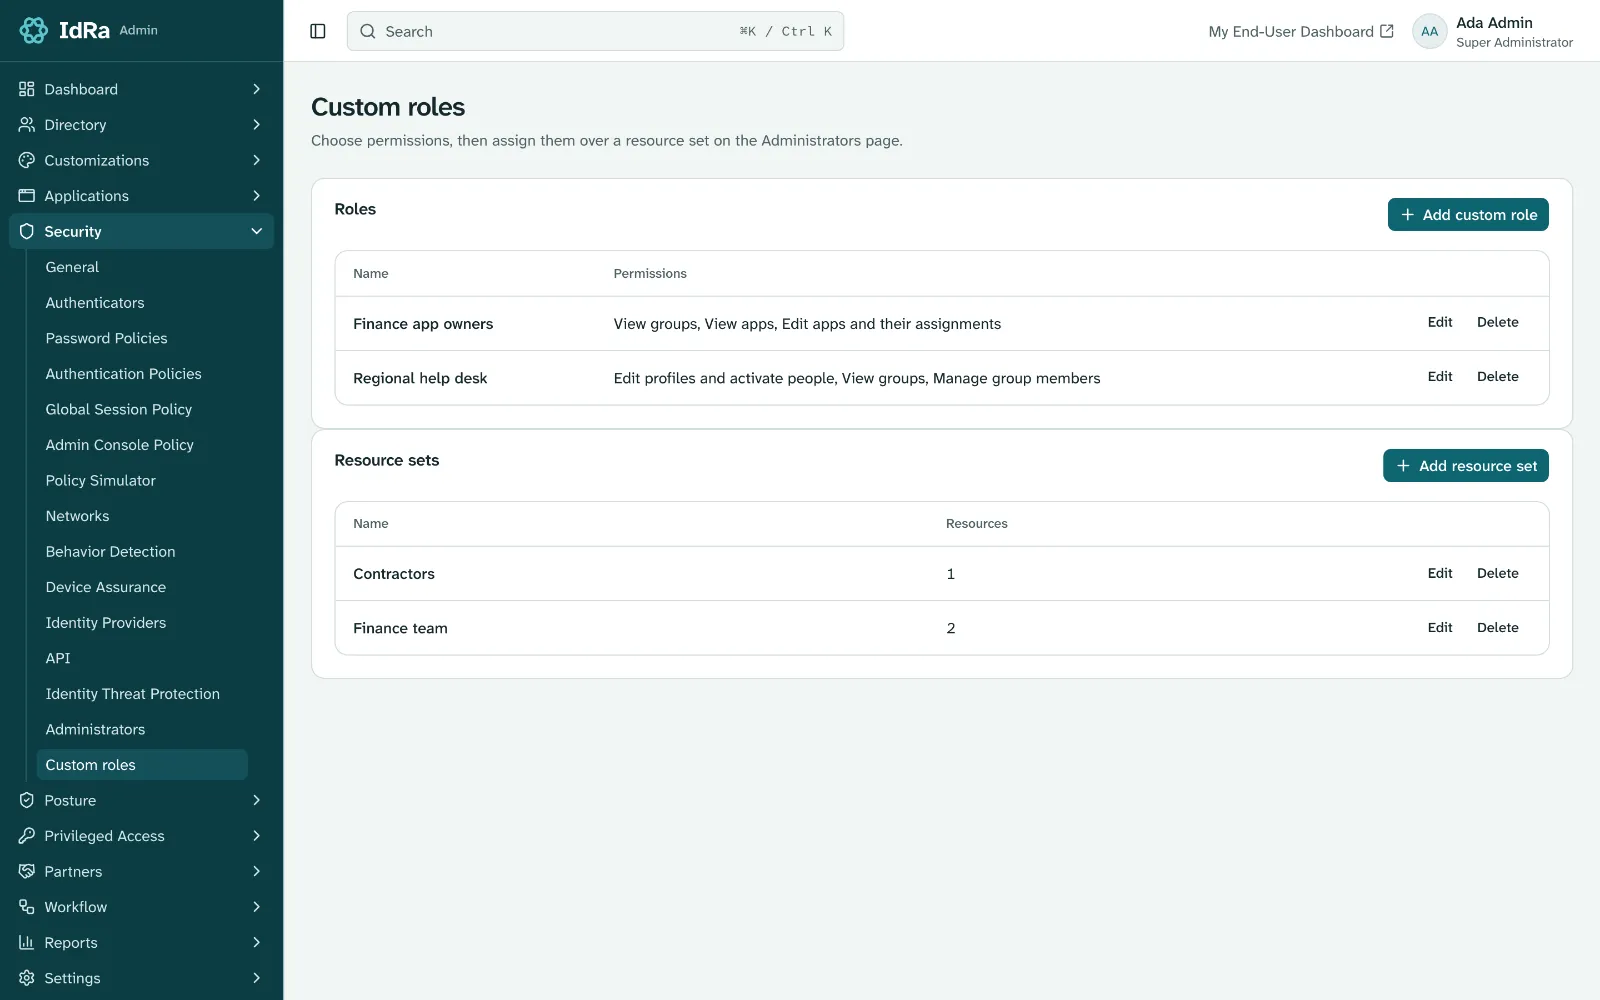
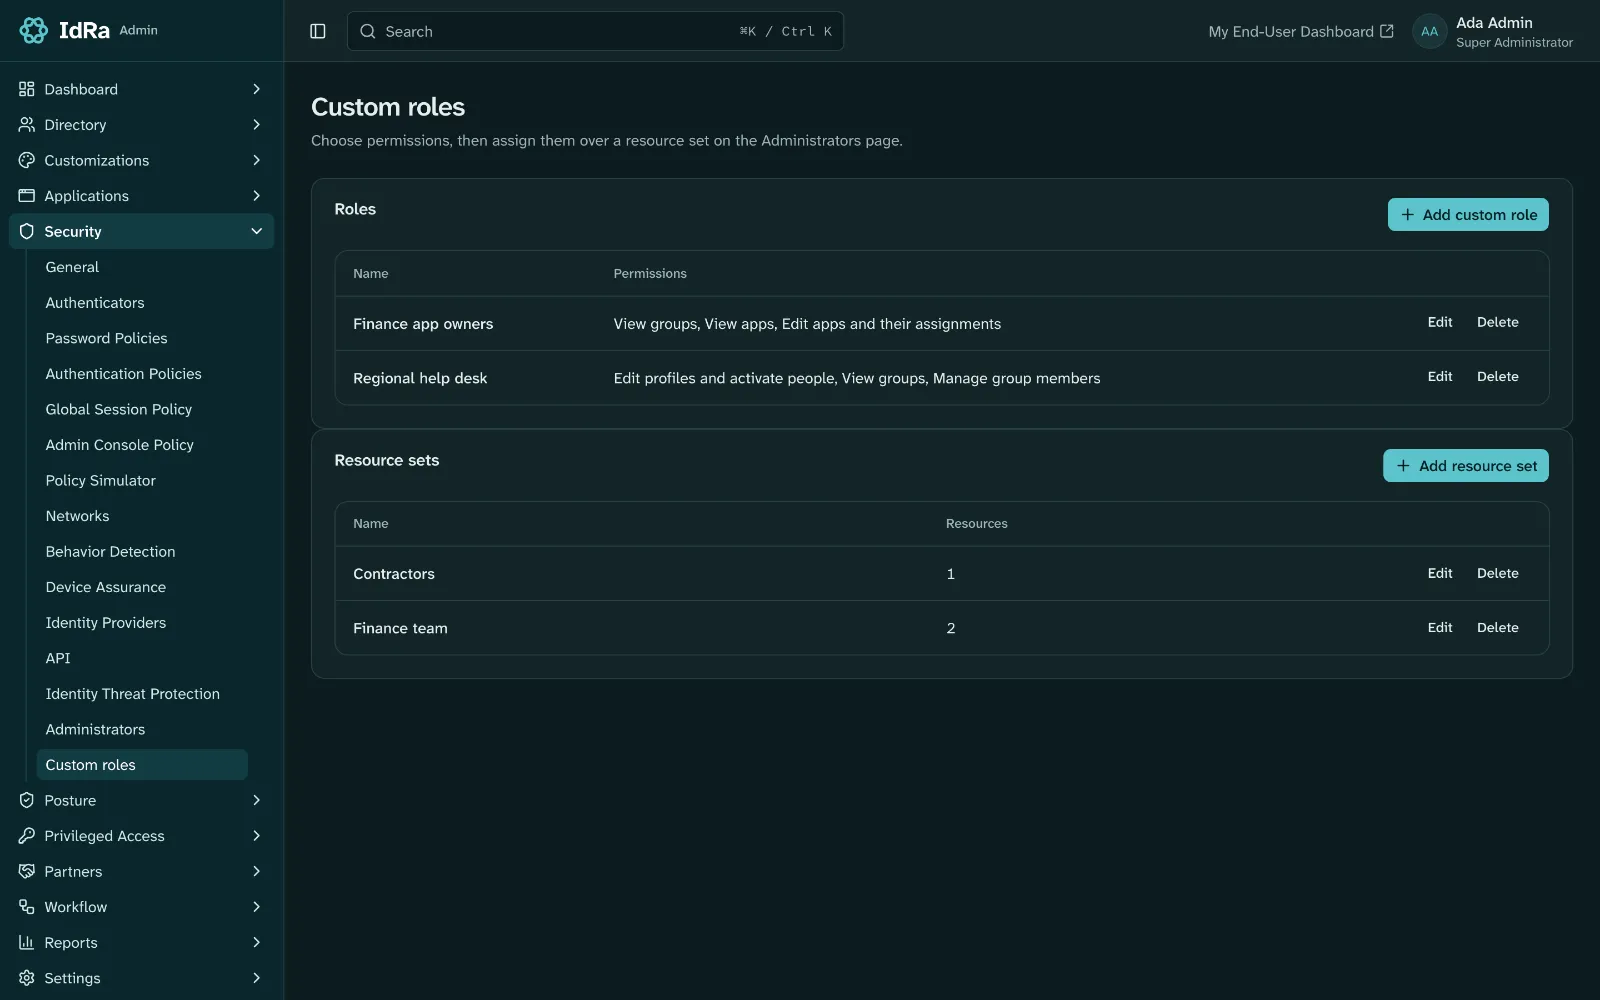
- 12 admin roles, and custom roles limited to a set of groups and apps
Every way to reach it
Use the admin console, CSV, SCIM, or the Okta-compatible API at /api/v1. An Okta importer brings people, groups and apps across.
- Search and filter with Okta’s operators on the API
- Reports for sign-in activity, MFA, app access denials and inactive people
Built on open standards.
- SCIM 2.0
- Okta Users and Groups API
Create your organization.
Pick an address and confirm your email, then sign in as its first admin. A setup wizard takes you through the rest.