Platform / MFA and adaptive access
Stronger proof when it matters.
Passkeys, push and authenticator apps, with rules on network, device and risk.
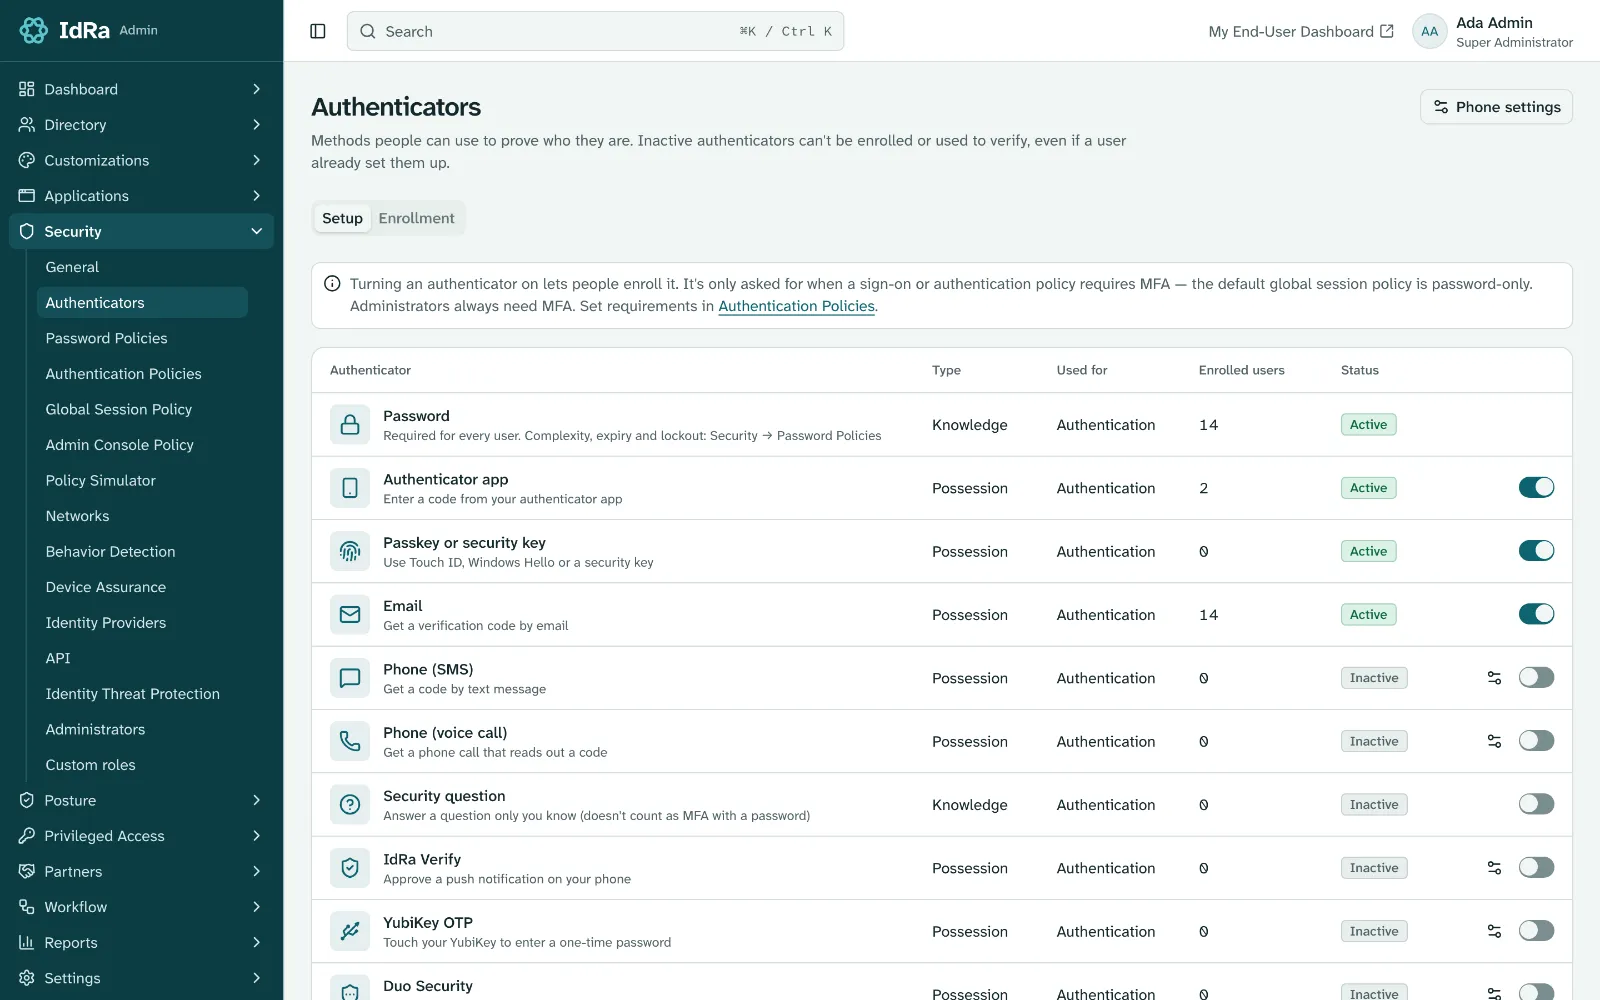
Eleven authenticators
Switch on the ones you trust, and decide per group which are required, optional or disabled.
- Phishing-resistant MFA with passkeys and security keys
- IdRa Verify push, with number challenge, browser, OS and location shown on the phone
- Authenticator apps (TOTP) and email codes
- SMS and voice through Twilio, YubiKey OTP, security questions
- Duo and RSA SecurID, if you already run them
- Any time-based token whose seed you hold, assigned per person
Policies that read the situation
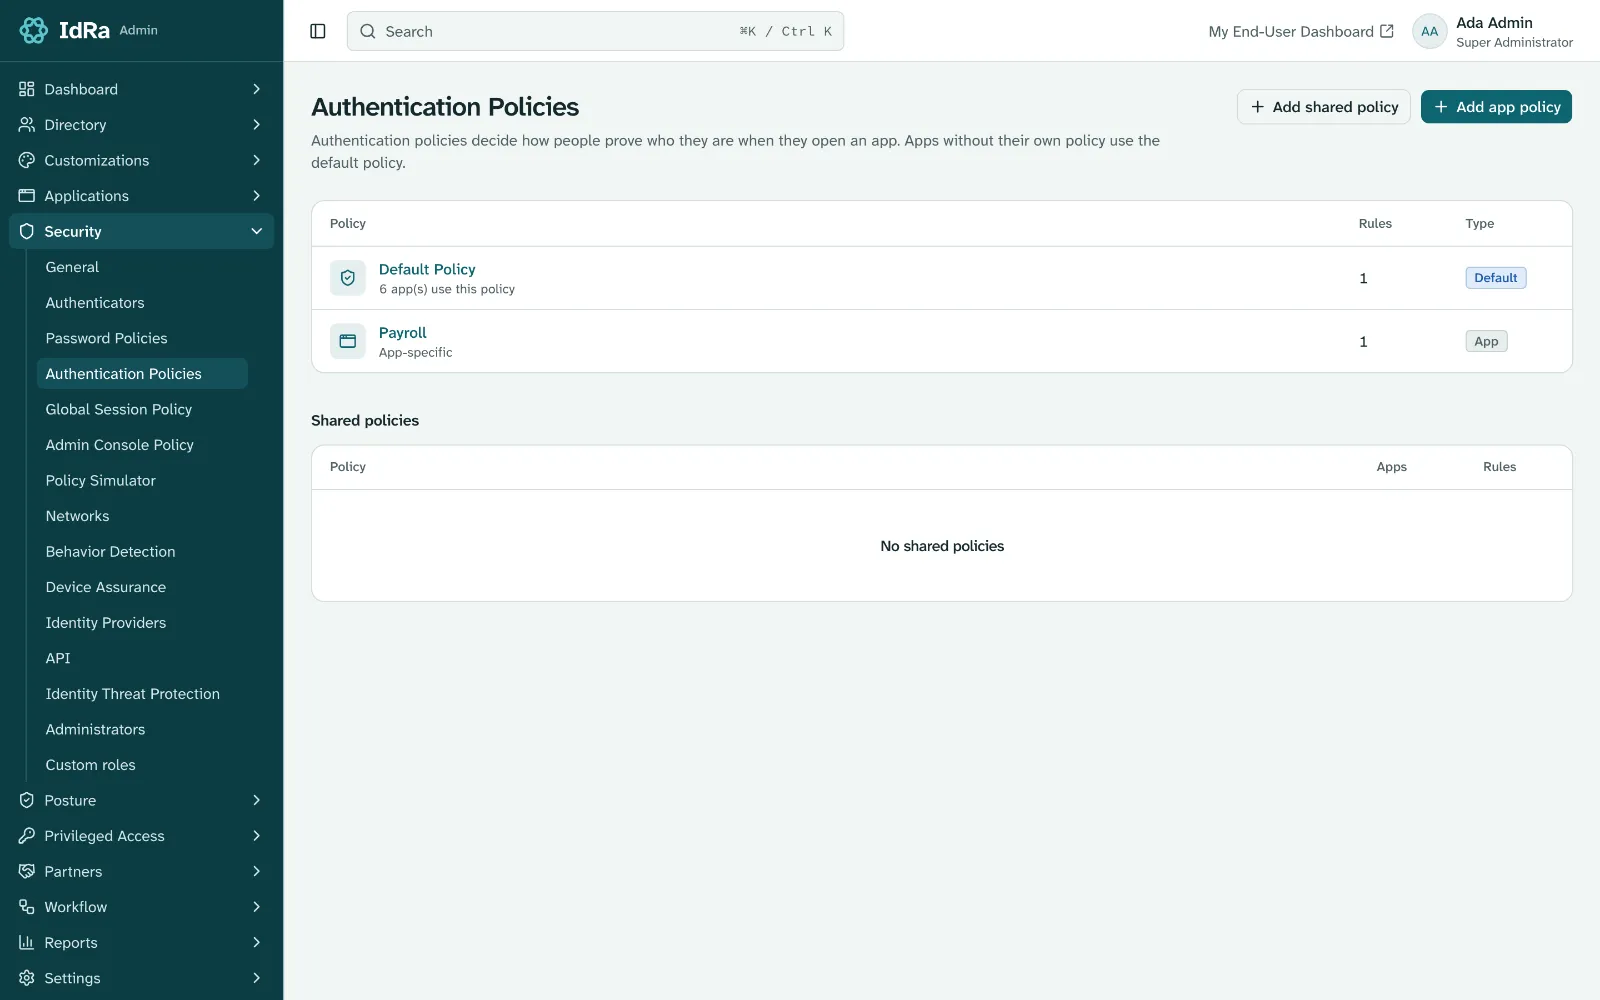
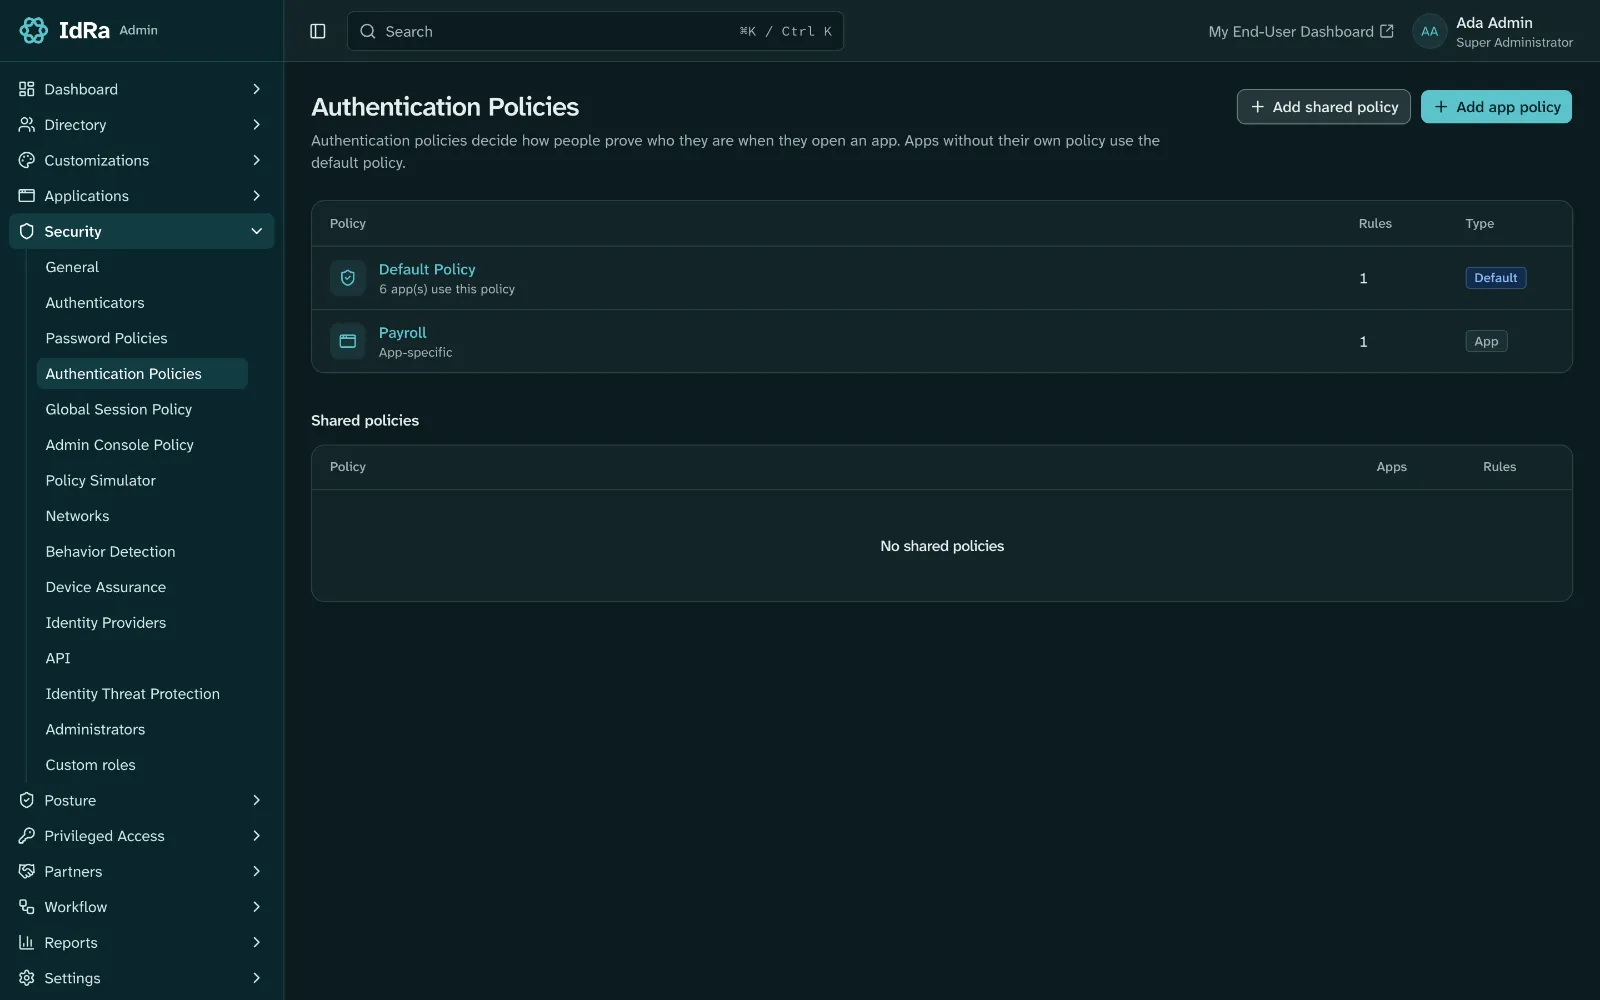
App sign-in rules run in order and match on groups, network zones, risk level, device state and platform. The first match decides: allow, deny or step up.
- IP zones, plus country, region, ASN and IP-category zones on deployments with Cloudflare or GeoIP files
- Three assurance levels: password, any second factor, phishing-resistant
- A re-authentication window per MFA rule
- A policy simulator, and shared policies across apps
Quiet protection at the door
Turn on threat feeds and CAPTCHA to stop known-bad traffic before a password is checked, and people hear about what happens on their account.
- Threat detection: public threat feeds plus a local password-spray detector
- CAPTCHA: Turnstile, hCaptcha or reCAPTCHA
- Lockout, rate limits, and recovery that never says whether an account exists
- Security emails with an “I don’t recognize this” link that raises the person’s risk
Built on open standards.
- WebAuthn
- FIDO2 passkeys
- TOTP
- Web Push
Create your organization.
Pick an address and confirm your email, then sign in as its first admin. A setup wizard takes you through the rest.