Platform / Single sign-on
One sign-in for every app.
Connect over OIDC, OAuth 2.1 or SAML 2.0, or put a gateway in front.
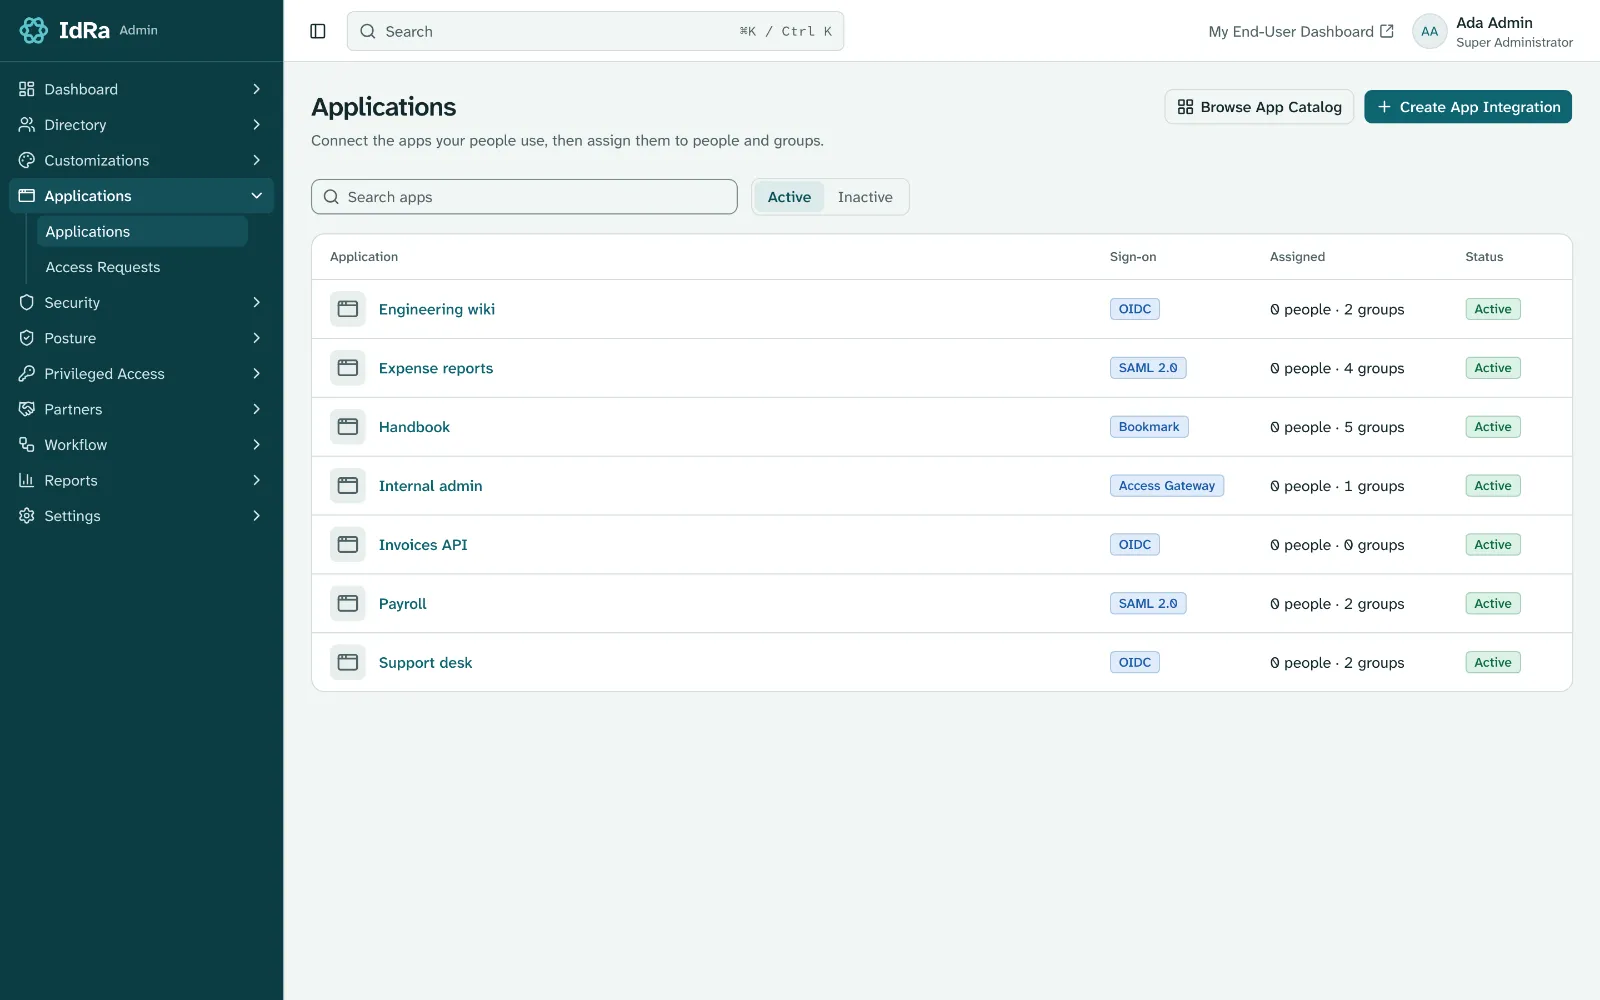
Every common way to connect an app
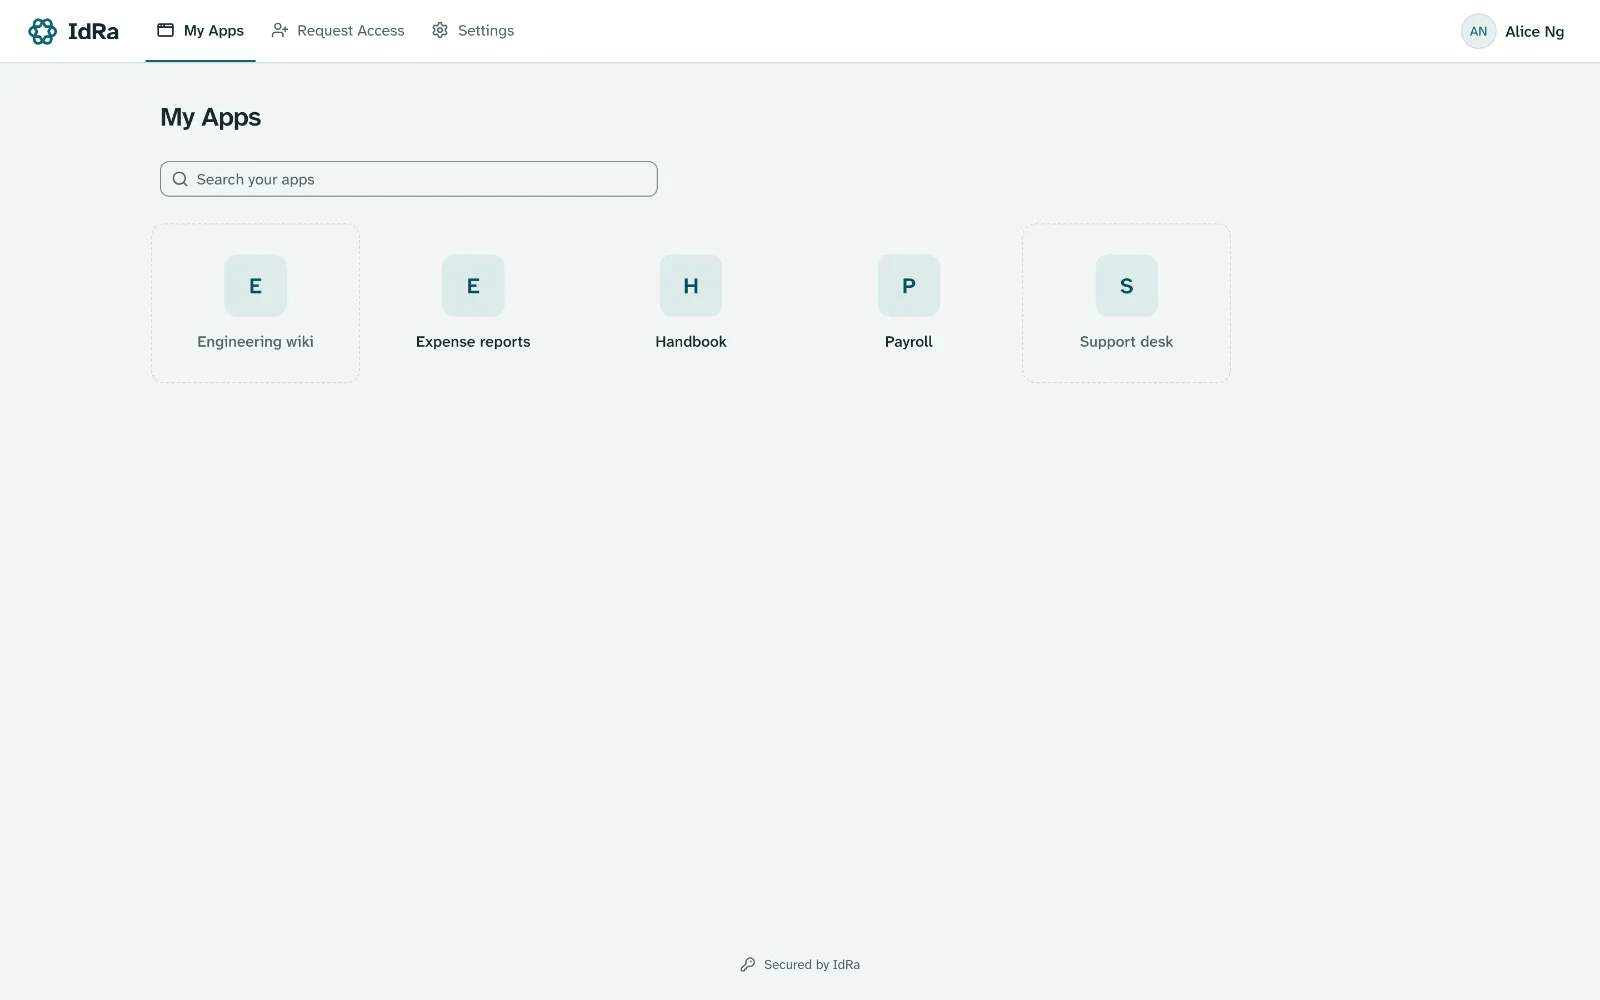
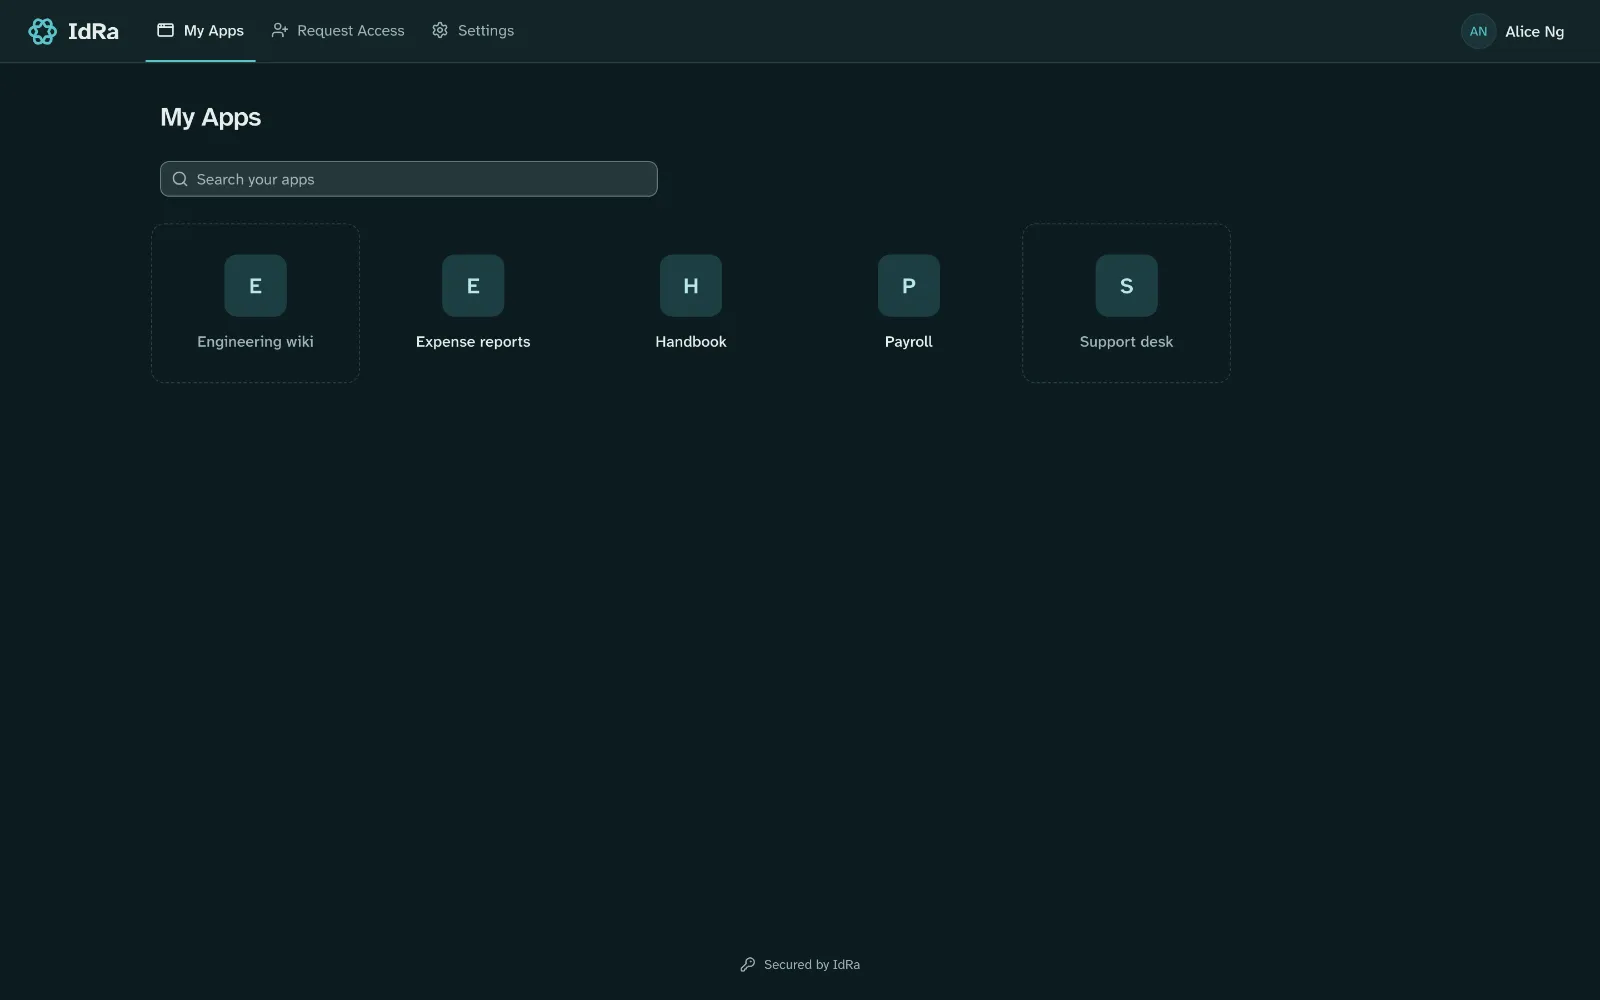
Add an app from the catalog’s templates, or configure it yourself. Assign it to people or groups and it appears on their dashboard.
- OIDC and OAuth 2.1: authorization code with PKCE, refresh tokens, client credentials, device code, private_key_jwt and DPoP.
- SAML 2.0: SP- and IdP-initiated sign-on, metadata import, attribute statements, encrypted assertions and per-app signing keys
- Forward-auth gateway for Caddy and nginx, with identity passed in headers you configure
- Bookmarks: a tile for anything else
- Local development: web and single-page apps accept http redirects on localhost, 127.0.0.1 or [::1] with a port
- Quickstarts for Next.js, Nuxt, SvelteKit, Express, React, Flask, FastAPI, Django, Go and SAML
Sign-out that reaches the app
OIDC apps get RP-initiated logout and back-channel logout, retried with backoff by a background job.
- End-session endpoint with post-logout redirect URIs
- SAML Single Logout when the app starts it, opt-in per app
- Refresh tokens rotate, and reusing an old one revokes the whole family
- Consent screens per app
Federate with the identity provider you already have
Send people to an external OIDC or SAML identity provider, or a Google or Microsoft preset. Route by domain, network zone, app or platform, and create accounts just in time.
- Generic OIDC and SAML identity providers
- Routing rules by domain, zone, app and platform
- Just-in-time creation, switchable per provider
Built on open standards.
- OpenID Connect
- OAuth 2.1
- SAML 2.0
- PKCE
- Back-channel logout
Create your organization.
Pick an address and confirm your email, then sign in as its first admin. A setup wizard takes you through the rest.