Platform / Security suite
See risky identities, then act.
Threat protection, posture management and privileged access, in the platform.
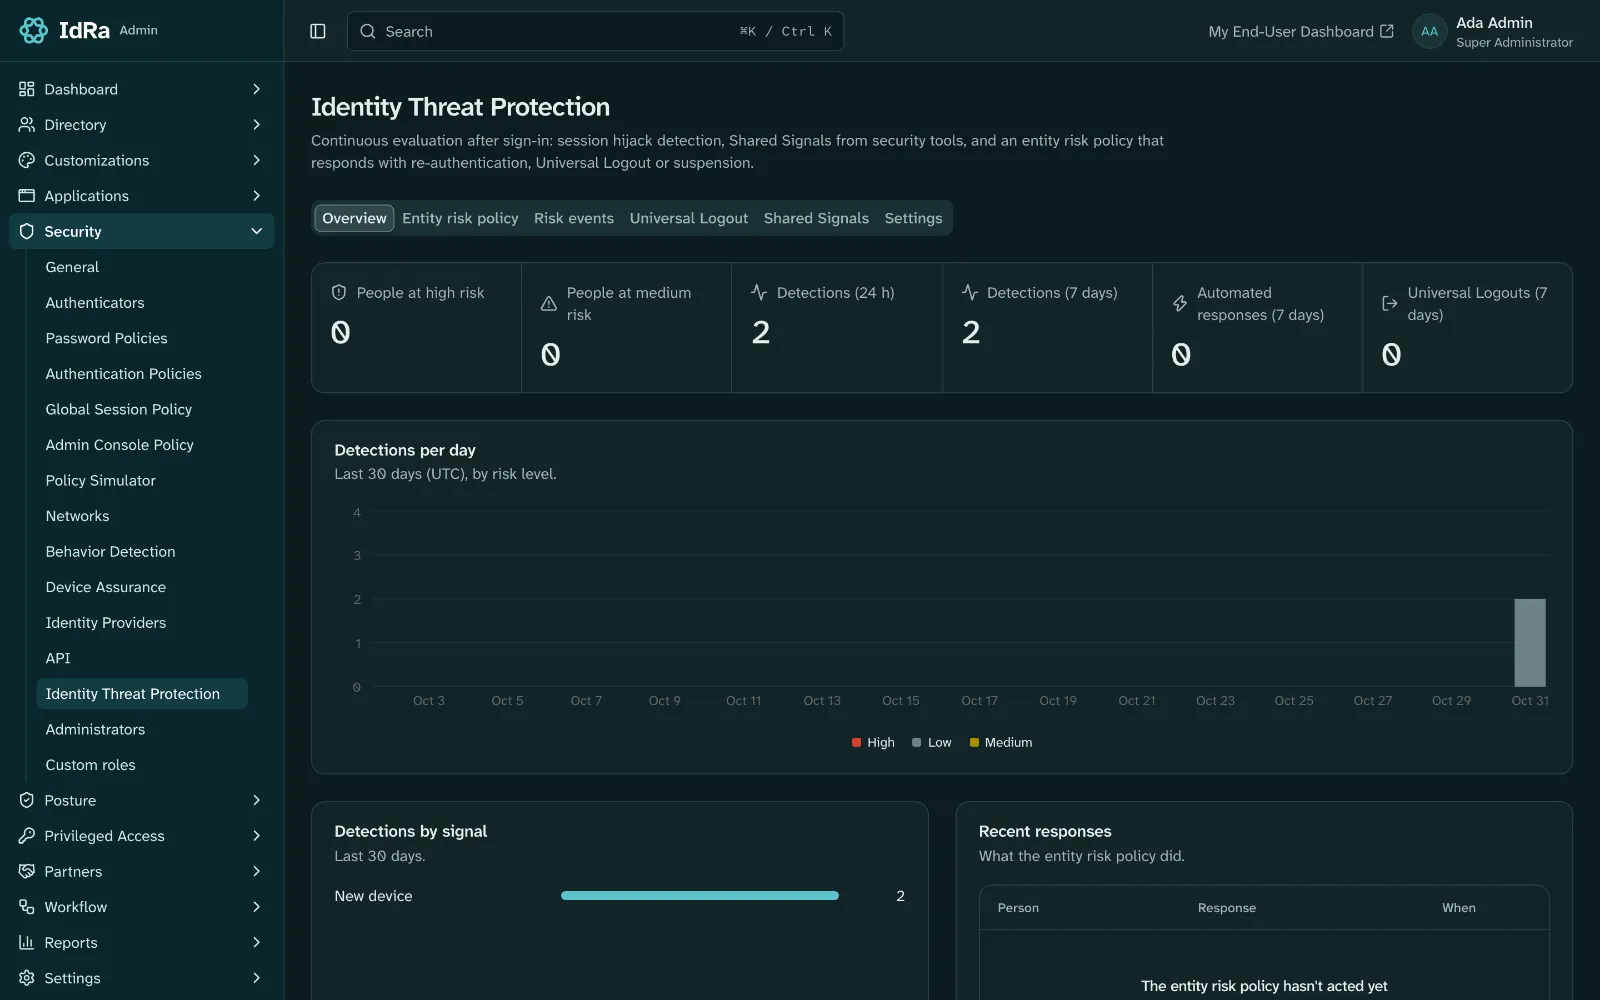
Threat protection
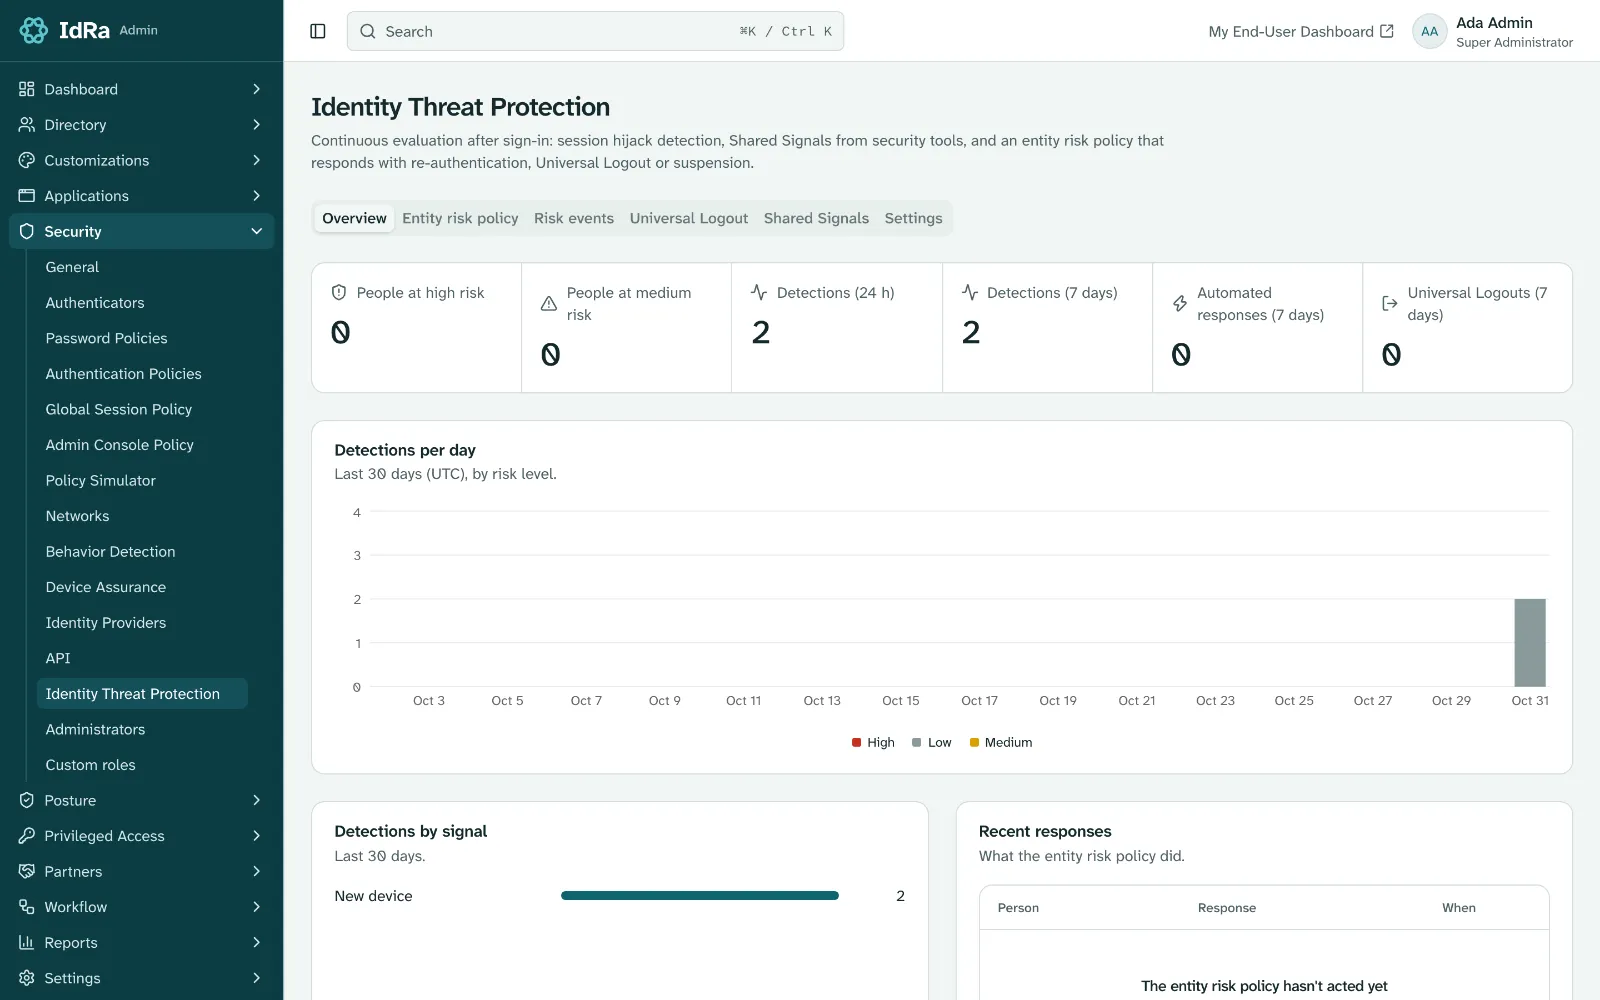
Detections raise a person’s risk. Your risk rules choose the response: notify, ask for MFA again, end the session, sign the person out everywhere or suspend.
- Global sign-out to OIDC apps, custom revocation endpoints, and Google, Microsoft, Okta, Slack Enterprise Grid and Zoom tenants once switched on
- Session hijack detection, and risk that decays on a schedule
- Shared Signals as both transmitter and receiver, with CAEP and RISC events
Identity security posture
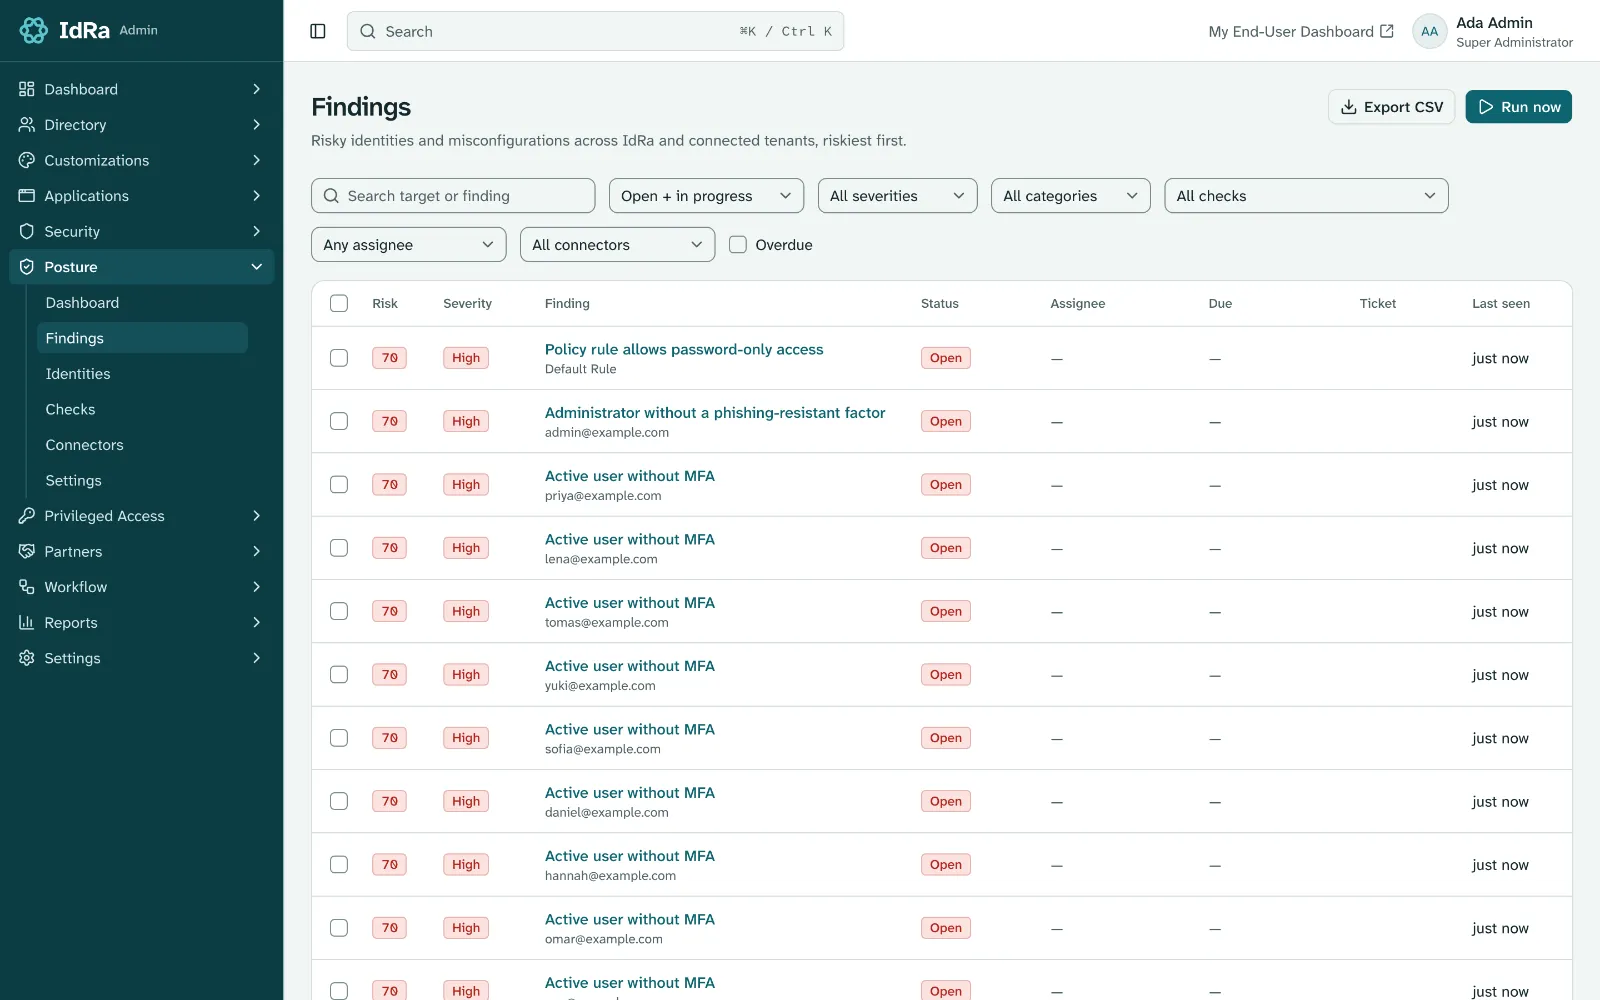
Connect your SaaS and cloud accounts to find what your identity provider can’t see, then fix it with confirmed actions or send a ticket.
- Connectors for GitHub, Google Workspace, Microsoft 365, AWS IAM, Salesforce, Slack, Okta, Atlassian and Zoom
- Findings for missing MFA, orphaned accounts, stale credentials and risky OAuth grants
- Fixed attack-path patterns, scored findings, and Jira or ServiceNow tickets
Privileged access
Replace long-lived SSH keys with short-lived certificates issued after MFA, and keep shared secrets in an encrypted vault.
- SSH certificates that last 10 minutes at most, through the idra CLI
- A vault with group-scoped reveal and an access log
- Time-limited access requests with an approver
Built on open standards.
- SSF
- CAEP
- RISC
- RFC 8935 and 8936
- OpenSSH certificates
Create your organization.
Pick an address and confirm your email, then sign in as its first admin. A setup wizard takes you through the rest.