Platform / Lifecycle and SCIM
Access from first day to last.
Bring people in over SCIM or CSV, then offboard them with one action.
In from your source of truth
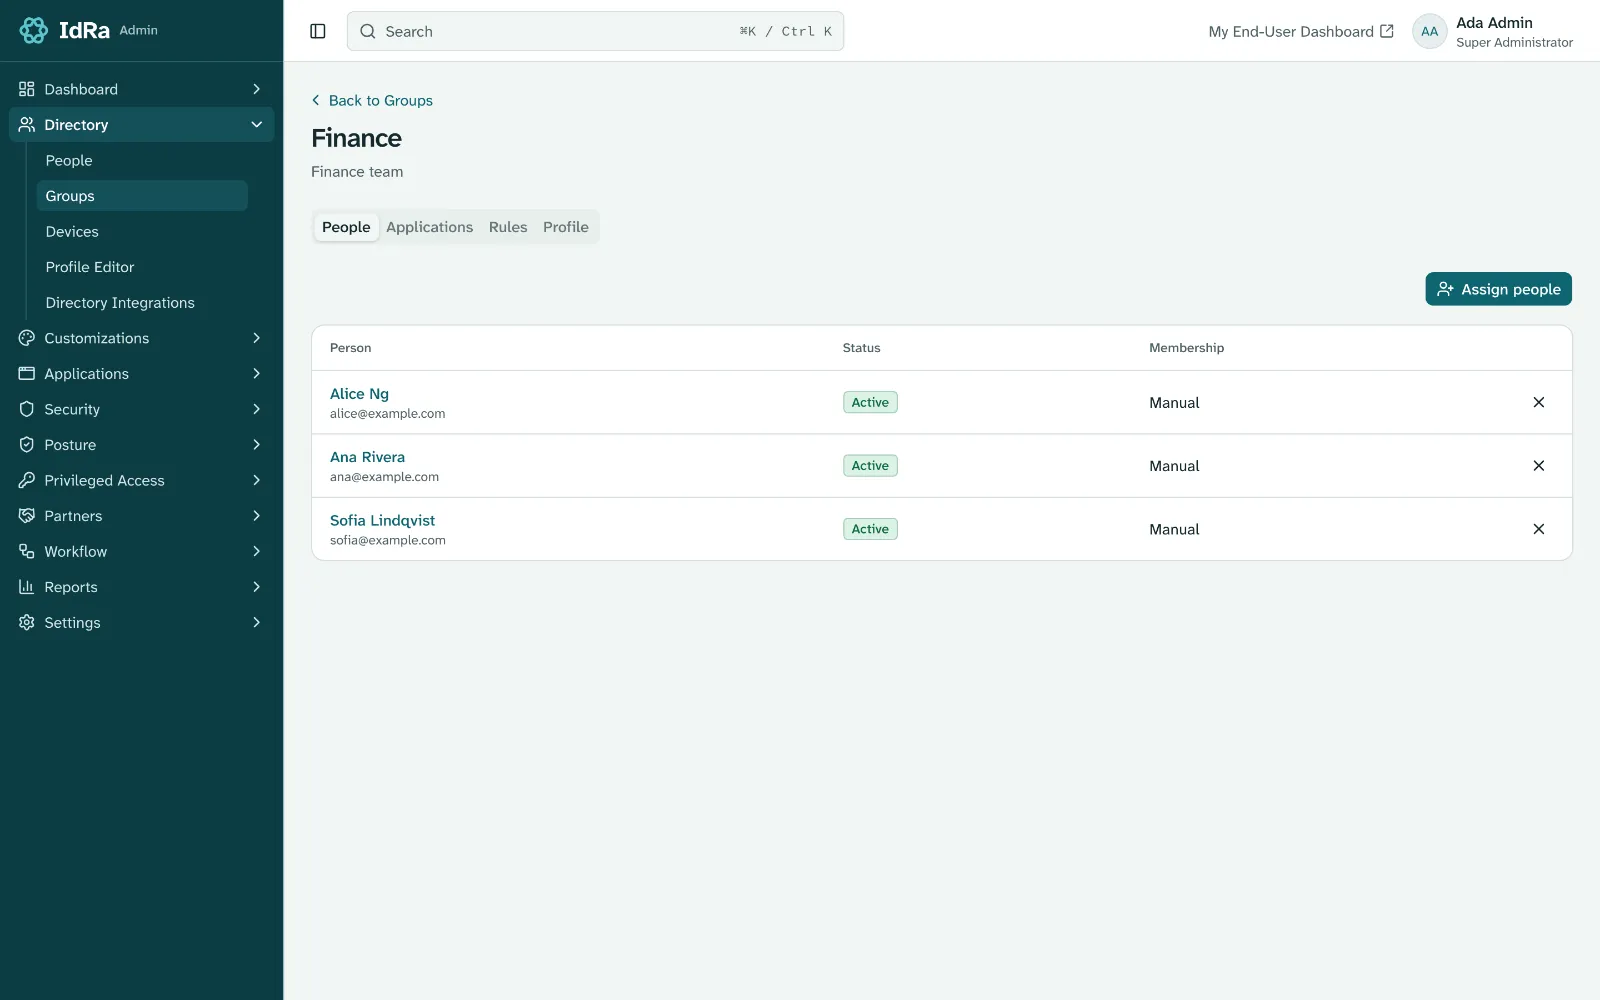
Point an HR system or another directory at IdRa’s SCIM server, or import a CSV with a preview before anything is written.
- Inbound SCIM 2.0 for users and groups, with PATCH and deprovisioning
- CSV import with column mapping, dry run and error export
- Group rules that assign people by attribute
Out to the apps you connect
Outbound SCIM creates, updates, deactivates and reactivates accounts in connected apps, and deletes them if you opt in, with retries and a history of every attempt.
- Outbound SCIM provisioning per app
- Push chosen groups or groups matching a name rule, or link to one already in the app
- SCIM attribute mapping per app, and a username format
- Import an app’s accounts over SCIM: you choose each link, create and removal, and removals over a limit, 20% by default, need a second confirmation
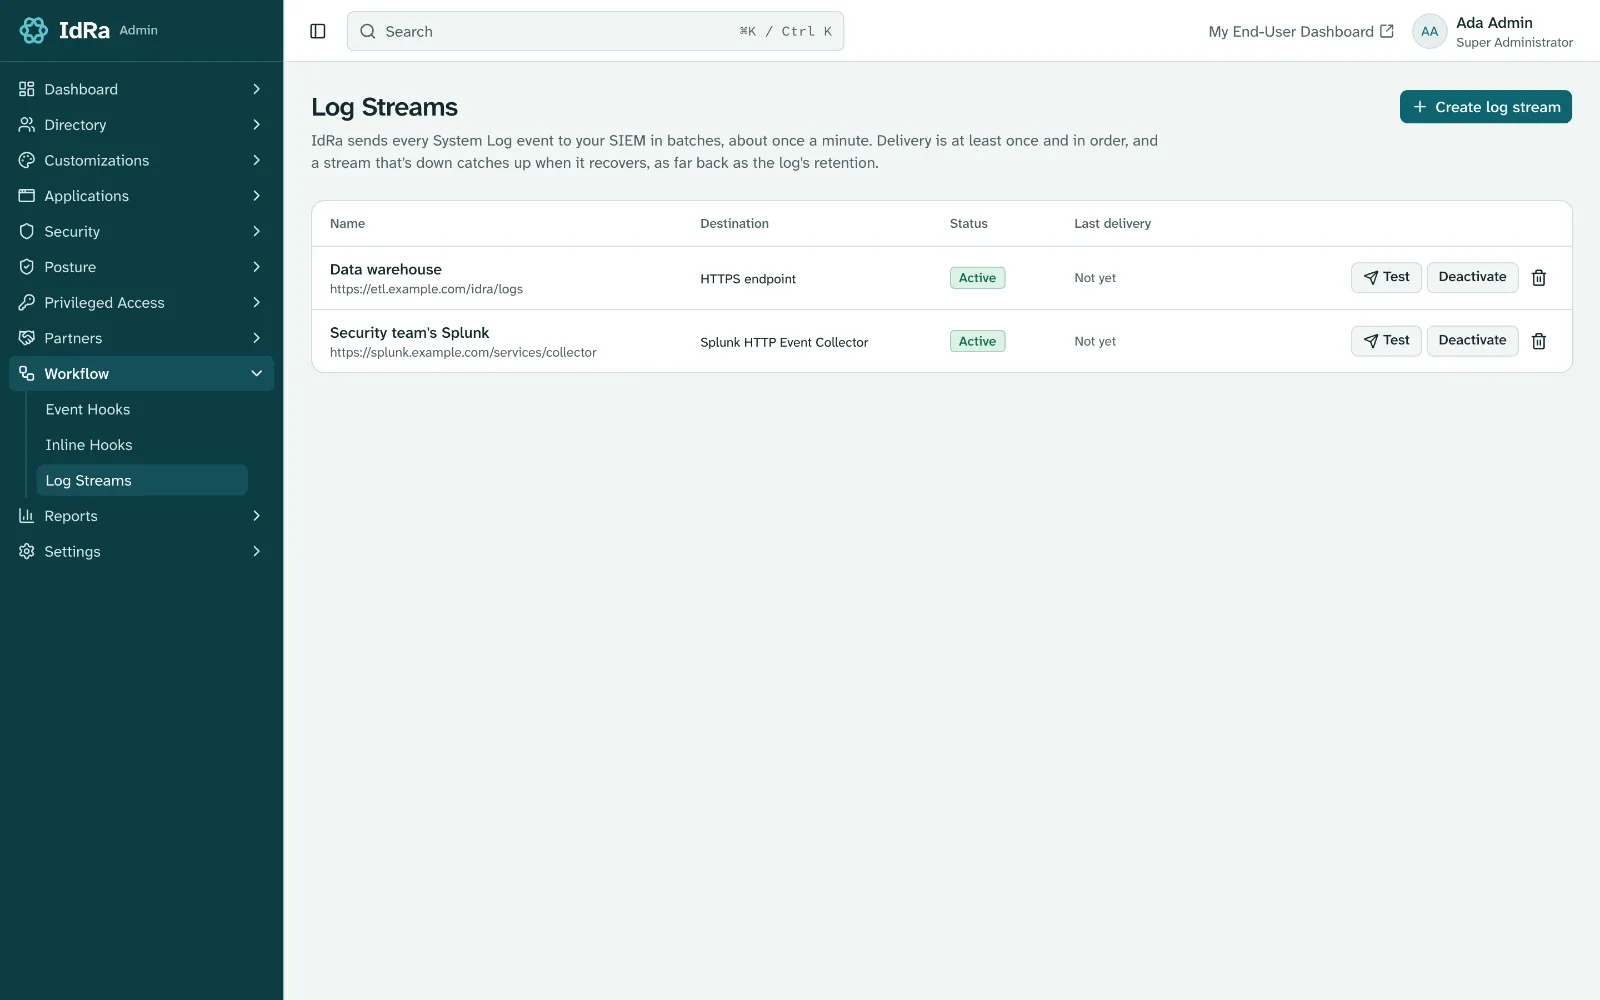
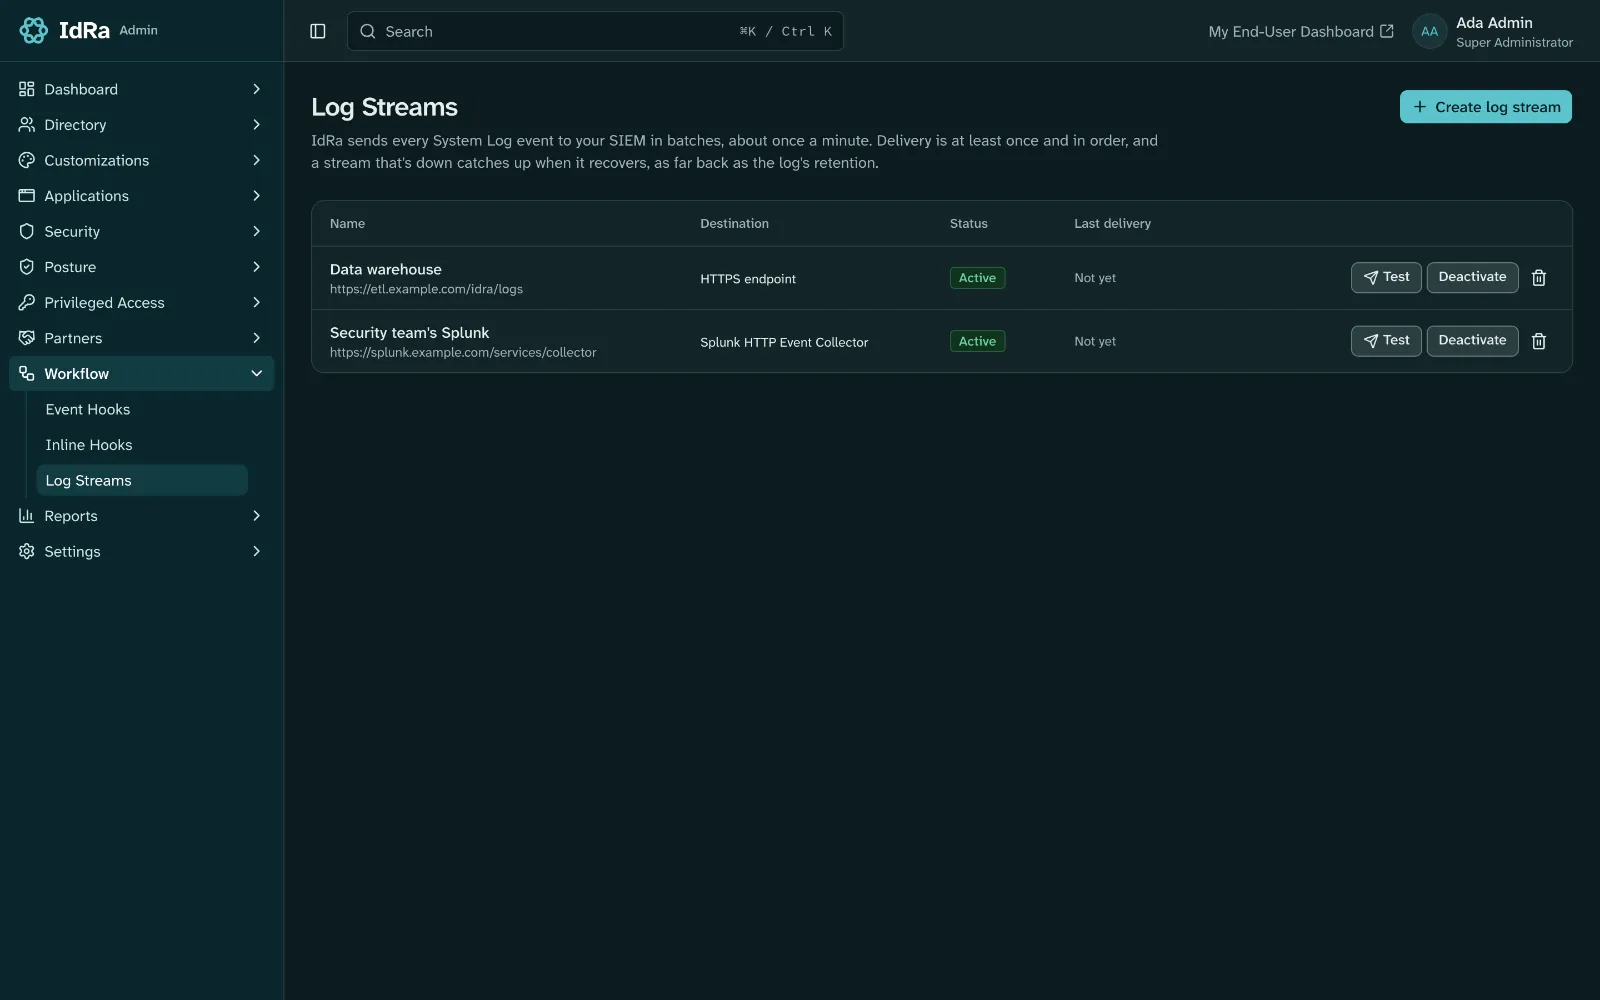
- Log streams to Splunk or any HTTPS endpoint
A last day that actually ends access
Deactivate someone once. IdRa ends their sessions, revokes their refresh tokens and tells OIDC apps with back-channel logout to sign them out.
- Time-limited group membership
- Access requests with an approver and an expiry
- Event hooks to your own systems, signed with HMAC and retried
Built on open standards.
- SCIM 2.0
- Signed webhooks
Create your organization.
Pick an address and confirm your email, then sign in as its first admin. A setup wizard takes you through the rest.